The State of AI Security 2026 Webinar: Oct 27th with Rinaldi Rampen and Jermey Snyder →
You'll find useful content about AI security, the cybersecurity landscape, news, events and much more updated regularly here.
Everyone is hunting the AI tools employees signed up for. The models and prompts your own teams wrote into the code, with the keys to call them, are the half nobody is looking at.
This is a broad release, and most of it is about precision. It sharpens who FireTail can attribute AI usage to, makes governance adaptive so it improves as your workforce uses AI, and adds harder access controls like restricting AI to corporate accounts.
New topic-based guardrail policies use FireTail's native topics. Policies you already run on the AWS equivalent keep working, with nothing to change.
Most AI monitoring can tell you something risky happened. Far fewer can tell you who did it, on which tool, in which exact words, without a week of correlation first.
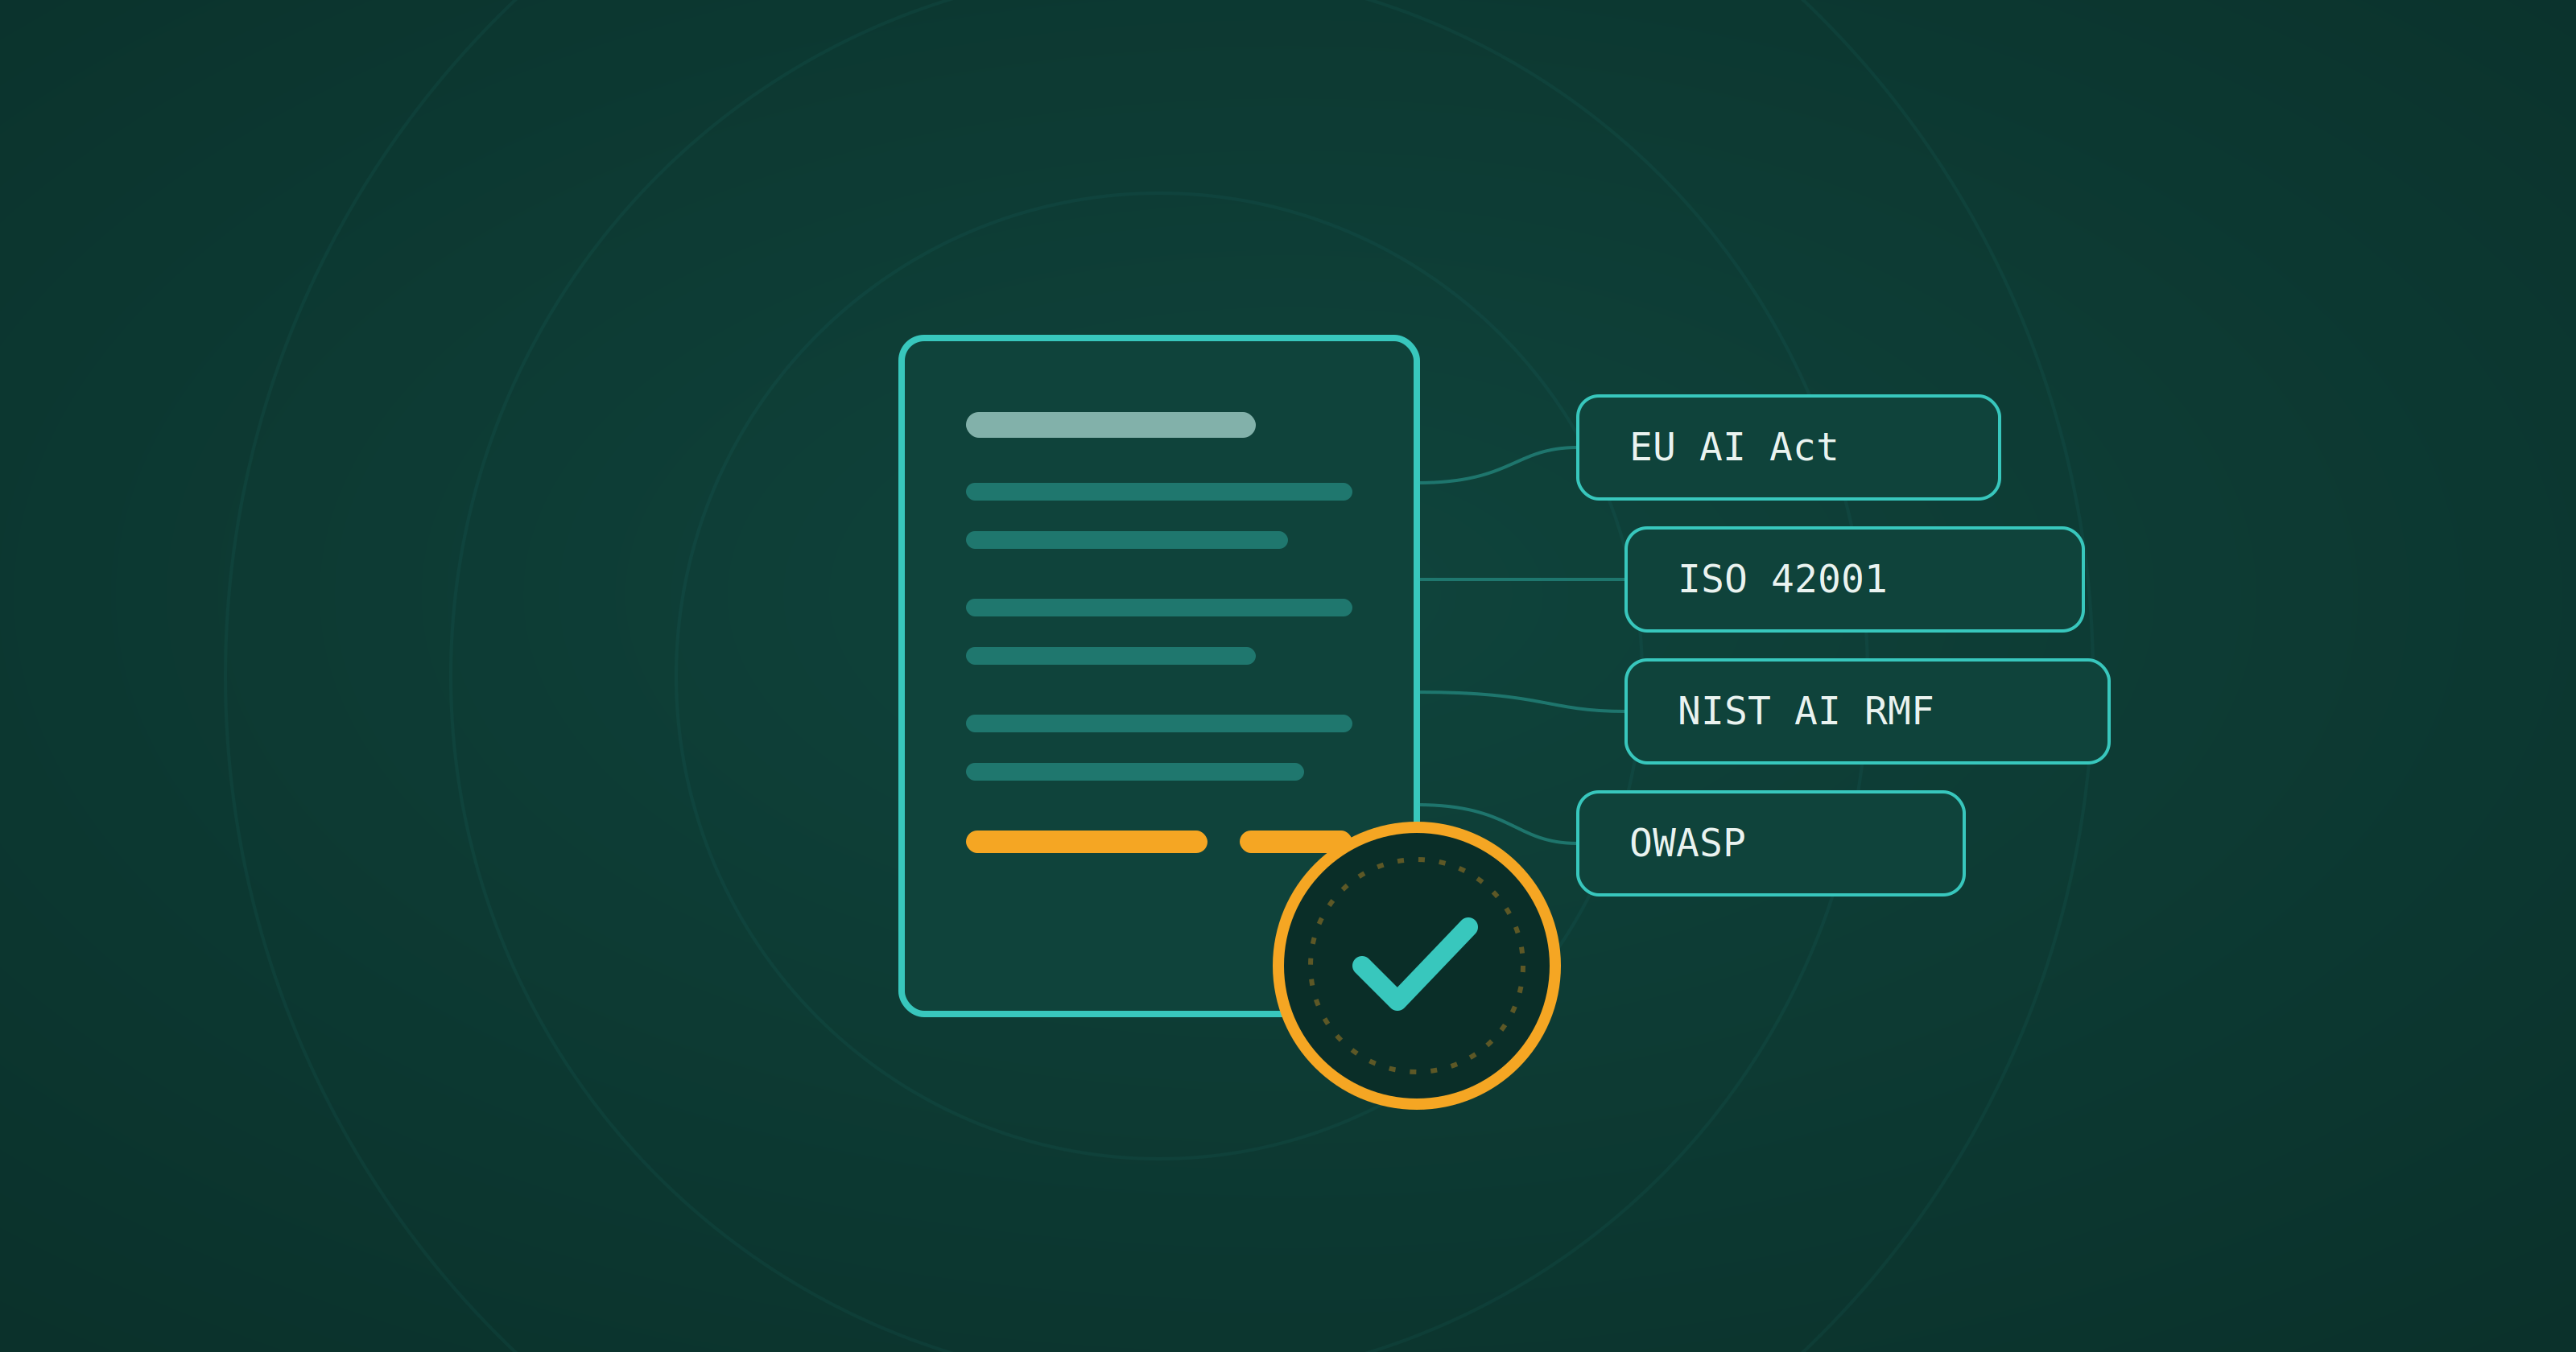
The frameworks are not the hard part. Proving that what you actually run lines up with them, on the day someone asks, is.
AI providers send one number a month. Cost observability is how you turn that into something you can forecast, attribute and defend.
If you prefer to be notified of new posts via email, simply subscribe to our blog below.